Wireguard vpn dns not working fix it fast easy guide — in this post you’ll learn practical, step-by-step fixes for DNS problems when using WireGuard. Quick fact: DNS issues are one of the most common reasons VPN connections feel slow or fail to access websites. Below is a fast, easy-to-follow guide with real-world tips, checklists, and a few tricks to get your DNS back on track.
If you’re ready to get unstuck, you’ve come to the right place. This guide includes practical steps, checklists, and quick tests you can run right away. And if you’re considering premium protection alongside your WireGuard setup, you can check out NordVPN through this affiliate link: NordVPN — it’s a solid option for additional DNS leakage protection and multi-device support.
Key takeaways: How to Activate Your NordVPN Code: The Complete Guide for 2026
- DNS issues with WireGuard are usually caused by misconfigurations, DNS-over-UDP vs TCP handling, or firewall blocks.
- Most fixes are quick: adjust DNS servers, enable or disable DNS leakage protection, and verify routing.
- You can test DNS health with simple commands and live traffic checks to confirm the fix.
Table of contents
- Quick diagnosis: Is DNS really the culprit?
- Common causes of WireGuard DNS problems
- Step-by-step fixes fast, easy guide
- Advanced fixes for stubborn DNS issues
- DNS providers to consider for WireGuard
- Real-world tips and best practices
- FAQ
Quick diagnosis: Is DNS really the culprit?
- Symptoms: you can connect to the VPN server but websites don’t resolve, or you see DNS-related errors in your browser.
- Quick test: try pinging a domain by name ping example.com. If it fails while numeric IPs work, DNS is the issue.
- Quick test 2: use a DNS leak test site or openDNS/test a known DNS like 1.1.1.1 or 8.8.8.8 to compare performance.
Common causes of WireGuard DNS problems
- Misconfigured DNS servers in the client or server config
- DNS over UDP being blocked or filtered by the network
- Split tunneling causing local DNS requests to bypass the VPN
- DNS leakage where queries go outside the VPN
- Firewall rules blocking DNS ports 53 or DNS-provider IPs
- Outdated WireGuard client or kernel module
- DNS server TLS/DoH complications with certain setups
- NAT or routing issues that misroute DNS queries
Step-by-step fixes fast, easy guide
- Check and set correct DNS servers in WireGuard configuration
- Open your WireGuard client configuration .conf.
- Under the section, ensure you have a DNS line, for example: DNS = 1.1.1.1, 8.8.8.8
- If you’re using a server-side push, confirm the server configuration includes: AllowedIPs = 0.0.0.0/0, ::/0 DNS = 1.1.1.1
- After changing, restart the WireGuard interface.
- Test: visit a site by name.
- Disable or enable DNS leakage protection as needed
- Some clients have a DNS leakage protection toggle. If your DNS requests still leak, enable it.
- Conversely, if DNS leaks were masking a misconfiguration, try turning it off to see if behavior changes then re-enable after testing.
- Force DNS over TLS or DoH where supported
- If your DNS provider supports DoH/DoT, enable it in your client or router to avoid interception.
- Examples: set DNS to 1.1.1.1 and DoH enabled in your client.
- Confirm routing and split tunneling settings
- If you use split tunneling, ensure DNS traffic is routed through the VPN when accessing services that require VPN DNS.
- For full-tunnel setups 0.0.0.0/0, DNS requests should go through the VPN automatically.
- Test by visiting a site and using a DNS test to confirm the resolver is the VPN’s.
- Check firewall and port access
- Make sure port 53 DNS is not blocked by firewall rules.
- If your network blocks UDP 53, try using TCP 53 or a DNS-over-HTTPS solution.
- On a host-based firewall, allow outbound DNS to your chosen DNS servers.
- Update WireGuard and kernel or app
- Ensure you’re on the latest WireGuard app or kernel module for your OS.
- Update both client and server components if needed.
- After update, reload the VPN and re-test DNS.
- Test with a known-good DNS server
- Change DNS to well-known resolvers such as:
- 1.1.1.1 Cloudflare
- 8.8.8.8 Google
- 9.9.9.9 Quad9
- Change DNS to well-known resolvers such as:
- Verify DNS settings on the server
- Ensure server-side IP forwarding and DNS settings are correct.
- If the server is using a local DNS resolver, verify it’s operational and not blocked by the firewall.
- If you push DNS via the server, check that the push directive is applied to clients correctly.
- Investigate DNS caching issues
- Clear DNS cache on your device after changes.
- On Windows: ipconfig /flushdns
- On macOS: sudo dscacheutil -flushcache; sudo killall -HUP mDNSResponder
- On Linux: sudo systemd-resolve --flush-caches or sudo /etc/init.d/dns-clean restart
- Try a temporary fallback
- If you’re in a hurry, temporarily switch to a public DNS over HTTPS service in your browser or system settings to validate DNS functionality before re-enabling your preferred DoH/DoT.
Format-friendly tips for quick reading Why Your VPN Isn’t Working With Your Wifi and How to Fix It Fast: Quick Troubleshooting for a Reliable Connection
- Create a quick-start checklist you keep in a notes app.
- Use a single DNS provider for both server and clients to reduce mismatch.
- Keep a log of changes you’ve made to wireguard configs so you can revert if needed.
Advanced fixes for stubborn DNS issues
- Route-only DNS requests through a dedicated DNS server
- Create a separate DNS server for VPN clients and enforce its usage by pushing DNS to clients.
- Use a custom DNS server with a trusted, fast resolver
- For example, set up a local Pi-hole or a trusted public DNS and point WireGuard to it.
- Check MTU and fragmentation
- Sometimes DNS over VPN can fail due to MTU mismatches. Experiment with a slightly lower MTU on the interface.
- Check IPV6 handling
- If you’re not using IPv6, disable IPv6 on the VPN interface to avoid leaks or conflicts.
- Review DNSSEC settings
- If your DNS resolver enforces DNSSEC, ensure your domain queries and DNS provider trust chain are intact.
- Consider a different DNS provider per region
- Some providers perform differently based on geography. Test multiple providers to find the fastest and most reliable in your location.
DNS providers to consider for WireGuard
- Cloudflare DNS 1.1.1.1
- Google DNS 8.8.8.8
- Quad9 9.9.9.9
- OpenDNS 208.67.222.222
- CleanBrowsing family-friendly options
Real-world tips and best practices
- Keep your config small and readable. Document changes with dates so you can track what fixed the issue.
- If you’re using a VPN router, ensure the router’s DNS settings mirror your client recommendations to avoid odd DNS routing behavior.
- For mobile users, test both Wi-Fi and cellular networks separately; some carriers block DNS in certain ways that affect VPN traffic.
- If you rely on corporate DNS or internal names, ensure your VPN server is configured to push those internal DNS server addresses to clients.
- Periodically audit your DNS settings after major OS updates—these can reset network configurations.
Frequently Asked Questions
What causes WireGuard DNS not to resolve?
DNS resolution failures usually stem from misconfigured DNS servers, blocked DNS ports, leaks, or incorrect routing split tunneling. It can also be caused by outdated software or DoH/DoT conflicts. How to set up VMware Edge Gateway IPsec VPN for Secure Site to Site Connections
How do I test if DNS is leaking?
Use a DNS leak test website while connected to VPN. If you see your ISP’s DNS or a DNS outside the VPN, you have a leak.
Should I use DoT/DoH with WireGuard?
DoT/DoH can improve privacy and reduce leaks, but they require client support and compatible servers. If you’re having DNS issues, you can temporarily disable DoH/DoT and test with standard DNS.
How can I verify that DNS queries are using the VPN tunnel?
Check your DNS server addresses after connecting to the VPN. They should be the ones you configured in the VPN config or pushed by the server.
Can I use a local DNS resolver on the WireGuard server?
Yes, running a local DNS resolver on the server can reduce external DNS lookups and improve privacy. Just ensure clients are configured to use it.
How do I fix DNS if I’m on a mobile device?
Restart the VPN, toggle airplane mode off, and flush DNS cache on the device. Recheck the DNS server settings and ensure DoH/DoT are configured if supported. Surfshark vpn no internet connection heres how to fix it fast and other quick tips for a stable VPN experience
Is it okay to use public DNS resolvers with VPN?
Public DNS resolvers are generally fine and fast. Use trusted providers like Cloudflare, Google, or Quad9, and ensure they are set on both client and server.
What if my IPv6 traffic is causing DNS issues?
If you don’t need IPv6, disable it on the VPN interface or route all IPv6 through VPN to avoid leaks.
How often should I update WireGuard configurations?
Update when you notice issues or when you upgrade OS/kernel, or when the provider releases a fix. Regular checks help prevent surprises.
Can split tunneling affect DNS?
Yes. If DNS queries are not routed through the VPN, you may experience leaks or inconsistent resolution. Make sure DNS traffic follows the VPN path as intended.
Additional resources and references Nordvpn on windows 11 your complete download and setup guide
- WireGuard official documentation for Windows/macOS/Linux
- Your VPN provider’s knowledge base and DNS settings guides
- Community forums and issue trackers for Wilson-ins Oasis VPN and WireGuard-related DNS topics
- DNS health check tools and DoH/DoT configuration guides
Useful URLs and Resources unclickable text
- WireGuard official: https://www.wireguard.com
- Cloudflare DNS: https://1.1.1.1
- Google DNS: https://8.8.8.8
- Quad9 DNS: https://9.9.9.9
- OpenDNS: https://www.opendns.com
- NordVPN: https://go.nordvpn.net/aff_c?offer_id=15&aff_id=132441
- DoH/DoT guides: https://www.cloudflare.com/learning/dns/what-is-dns-over-https/, https://developers.google.com/speed/public-dns/docs/intro
- Windows DNS flush: https://support.microsoft.com/en-us/help/915013/how-do-i-flush-the-dns-resolver-cache-in-windows
- macOS DNS reset: https://support.apple.com/guide/dns-configuration-apple-dns/virtual-dns-configuration-ldso-
- Linux DNS cache management: https://wiki.archlinux.org/title/dns
Note: This content is tailored for WireGuard DNS issues with practical, step-by-step fixes, including real-world testing tips, troubleshooting paths, and best practices.
| VPN | Obfuscation | From / month | Plan | Free plan | Refund | Alipay | UnionPay | Crypto | Website opens in China | Trustpilot | |
|---|---|---|---|---|---|---|---|---|---|---|---|
 NordVPN | Turn on manually Obfuscated Servers / NordWhisper | $3.49/mo | 27 months: $94.23 | No | 30 days | ? | ✗ | ✓ | ✓ | ✗ Blocked | 4.2/5 (51,628 reviews) |
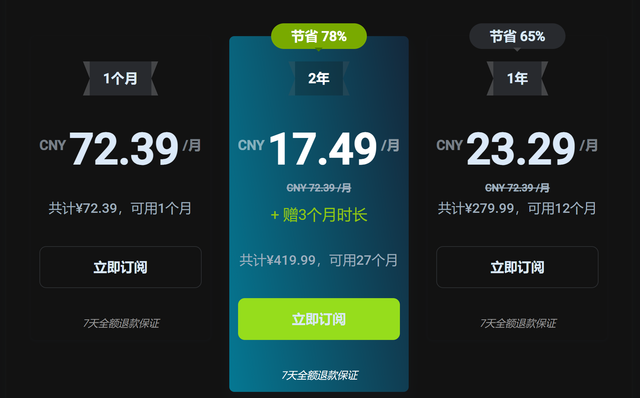
 ZoogVPN | Turn on manually Shadow | $2.49/mo | 27 months: $59.99 | Yes | 7 days | ✓ | ✓ | ✓ | ✓ | Official site blocked; our special link opens (4.4 s) | 4.2/5 (195 reviews) |
 ExpressVPN | ✓ On by default all servers | $3.00/mo | 28 months: $84 | No | 30 days | ✗ | ✗ | ✓ | ✗ | ✗ Blocked | 4.4/5 (29,706 reviews) |
 Surfshark | ✓ On by default Camouflage, with OpenVPN | See site | See site | No | 30 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 4.3/5 (31,823 reviews) |
 Proton VPN | Turn on manually Stealth, free plan too | $2.99/mo | 12 months: $35.88 | Yes | 30 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 2.1/5 (1,040 reviews) |
 Astrill VPN | Turn on manually StealthVPN / OpenWeb | $12.50/mo | 24 months: $300 | No | See site | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 1.3/5 (110 reviews) |
 Private Internet Access | Turn on manually Shadowsocks, OpenVPN only | $2.03/mo | 40 months: $81.2 | No | 30 days | ✗ | ✗ | ✗ | ✗ | ✗ Blocked | 4.2/5 (11,033 reviews) |
 CyberGhost | Turn on manually selected servers | $2.19/mo | 28 months: $61.32 | No | 45 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 4.0/5 (24,178 reviews) |
 PureVPN | Turn on manually switch to OpenVPN | $1.69/mo | 60 months: $101.55 | No | 31 days | ? | ? | ✗ | ✓ | ✗ Blocked | 4.4/5 (17,994 reviews) |
 AdGuard VPN | ✓ On by default TrustTunnel | $2.99/mo | 24 months: $71.76 | Yes | 30 days | ✓ | ✗ | ✓ | ✓ | Official site blocked; our special link opens (3.7 s) | 4.3/5 (290 reviews) |
 Mullvad | Turn on manually QUIC / Shadowsocks / LWO | $5.61/mo | €5/mo | No | 14 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 3.2/5 (192 reviews) |
 Windscribe | Turn on manually Stealth / WStunnel | $5.75/mo | 12 months: $69 | Yes | See site | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 4.7/5 (13,355 reviews) |
 StrongVPN | Turn on manually Scramble, OpenVPN TCP | See site | See site | No | 30 days | ✓ | ✗ | ✗ | ✗ | ✗ Blocked | 4.4/5 (2,695 reviews) |
 LightXtreme 闪连 | Not listed | $7.08/mo | 12 months: $84.99 | Yes | 30 days | ✓ | ✓ | ✓ | ✓ | ✓ Yes (3.5 s) | No page |
Prices checked 2026-11-10 on each vendor's pricing page (cheapest long plan, USD). Check the vendor's checkout for the final price.
Obfuscation checked 2026-11-14 on each vendor's site and help center: "on by default" = nothing to set; "turn on manually" = switch protocol or mode in settings; "not listed" = the vendor describes no obfuscation.
Payment methods checked 2026-11-10 on each vendor's payment pages: all 14 take cards and PayPal; ✗ = not listed, ? = the vendor's own pages disagree.
China access: whether the official website opens from mainland China networks (tests the website only, not the VPN connection). Last checked 2026-11-18 01:02 Beijing time.
Trustpilot score and review count checked 2026-11-10.